
Risk and Compliance: GRC vs ERM for Managing Enterprise Risk
GRC should manage controls, compliance, and governance discipline, while ERM should manage the full risk picture across strategy, operations, finance, cyber, legal, and external threats. Treating them as the same thing creates gaps, duplicated work, and slow reporting. The stakes are real: IBM reported that the global average cost of a data breach reached $4.88 million in 2024 [source: IBM]. That number shows why risk work cannot sit in scattered spreadsheets or isolated audit folders.
TLDR: GRC is best for proving that rules are followed, controls are tested, and regulatory duties are handled. ERM is broader; it helps leadership decide which risks could hurt growth, cash flow, reputation, or resilience. For example, a bank may use GRC to track 2,000 control tests, while ERM ranks the top 15 enterprise risks and shows that cyber fraud could cause a 7% revenue hit in a severe event. The strongest companies use both, with clear ownership and shared data.
What GRC Means
GRC stands for governance, risk, and compliance. In practice, it is often the operating system for policies, controls, audits, regulatory obligations, third-party reviews, and issue tracking. It answers a direct question: Is the organization doing what it said it would do, and can it prove it?
GRC is usually led by compliance, internal audit, legal, information security, or risk control teams. Its work is structured and evidence based. A GRC program may track access reviews, vendor assessments, privacy controls, anti bribery training, audit findings, or policy exceptions.
- Governance: roles, approvals, committees, policies, and accountability.
- Risk: control risks, operational risks, IT risks, and compliance risks.
- Compliance: laws, regulations, standards, frameworks, and proof of adherence.
The value of GRC is consistency. It reduces confusion over who owns a control, when testing is due, and which findings are still open. The irritating part is that many GRC tools make simple tasks feel heavy. Risk teams often say it feels absurd when uploading one audit evidence file takes eight clicks and a 20 second screen refresh.
What ERM Means
ERM stands for enterprise risk management. It looks at risk from the board and executive level. ERM asks a wider question: What could stop the organization from reaching its goals?
ERM covers risks that may not fit neatly into a compliance checklist. These include market shifts, supply chain failure, interest rate changes, climate exposure, talent shortages, geopolitical shocks, product quality failures, cyber attacks, acquisitions, fraud, and reputational harm.
ERM works best when it connects risk to strategy. For example, if a retailer plans to expand into three new countries, ERM should assess currency risk, labor rules, logistics weakness, data privacy exposure, and brand risk before the investment is approved. That is different from checking whether a policy was read by employees.
GRC vs ERM: The Core Difference
The simplest difference is scope. GRC is control centered. ERM is decision centered. GRC proves that defined controls and obligations are being managed. ERM helps leaders decide which risks deserve money, time, attention, or acceptance.
| Area | GRC | ERM |
|---|---|---|
| Main focus | Policies, controls, compliance, audits | Strategic and enterprise wide risk |
| Primary users | Compliance, audit, legal, security | Board, executives, risk committees |
| Typical output | Control reports, issue logs, evidence files | Risk appetite, heat maps, scenarios, risk reports |
| Time horizon | Current obligations and recurring reviews | Short, medium, and long term threats |
This split matters because a company can be compliant yet still fragile. It may pass an audit and still depend on one supplier for 80% of a critical component. GRC may show that the supplier assessment was completed. ERM should ask what happens if that supplier shuts down for six weeks.
Where GRC and ERM Overlap
GRC and ERM are not rivals. They feed each other. GRC supplies hard evidence about controls, findings, incidents, and obligations. ERM turns that information into higher level insight for executives and the board.
For instance, repeated control failures in access management may appear as minor audit issues in a GRC tool. ERM may group them into a larger cyber resilience risk. If the failures affect customer data, payment systems, and remote admin access, the risk profile changes fast.
Good integration reduces duplicate surveys and scattered reporting. Without it, business units may receive separate requests from audit, compliance, security, privacy, and enterprise risk. Honestly, it feels like risk work becomes a tax on the business when five teams ask the same manager for nearly identical answers in different templates.
When GRC Should Lead
GRC should lead when the issue is tied to rules, controls, evidence, or required procedures. This includes regulatory reporting, audit remediation, training attestations, policy management, vendor due diligence, and control testing.
Common GRC use cases include:
- Tracking compliance with privacy, financial, safety, or industry rules.
- Testing controls for access, change management, approvals, and segregation of duties.
- Managing audit findings and remediation plans.
- Collecting evidence for regulators, auditors, or customers.
- Monitoring third-party compliance requirements.
GRC creates discipline. It keeps proof close to the process. That matters when a regulator, auditor, insurer, or major customer asks for documentation with little warning.
When ERM Should Lead
ERM should lead when the organization faces uncertainty that may affect strategy, capital allocation, reputation, or long term performance. These issues need executive judgment, not only control testing.
Common ERM use cases include:
- Setting risk appetite by risk category.
- Ranking top enterprise risks for the board.
- Running scenarios for outages, recessions, cyber incidents, or supply disruption.
- Assessing risk in mergers, expansion plans, and major investments.
- Linking risk exposure to financial impact and business goals.
ERM helps leadership compare risks that look nothing alike. A cyber event, a credit shock, a product recall, and a labor shortage cannot be managed well with the same checkbox. ERM gives them a common frame: likelihood, impact, velocity, readiness, ownership, and risk appetite.
How Companies Should Use Both
The best model is connected but not blurred. GRC owns the control layer. ERM owns the enterprise view. Both should use shared taxonomies, shared risk categories, and common reporting rules.
A practical structure may look like this:
- Define risk categories: operational, cyber, compliance, financial, strategic, legal, reputational, and third-party.
- Map controls to risks: each key control should connect to a risk that matters.
- Set ownership: process owners manage controls, executives own top risks.
- Agree on scoring: use common ratings for impact, likelihood, and control strength.
- Report at two levels: detailed GRC dashboards for control teams, concise ERM reports for leadership.
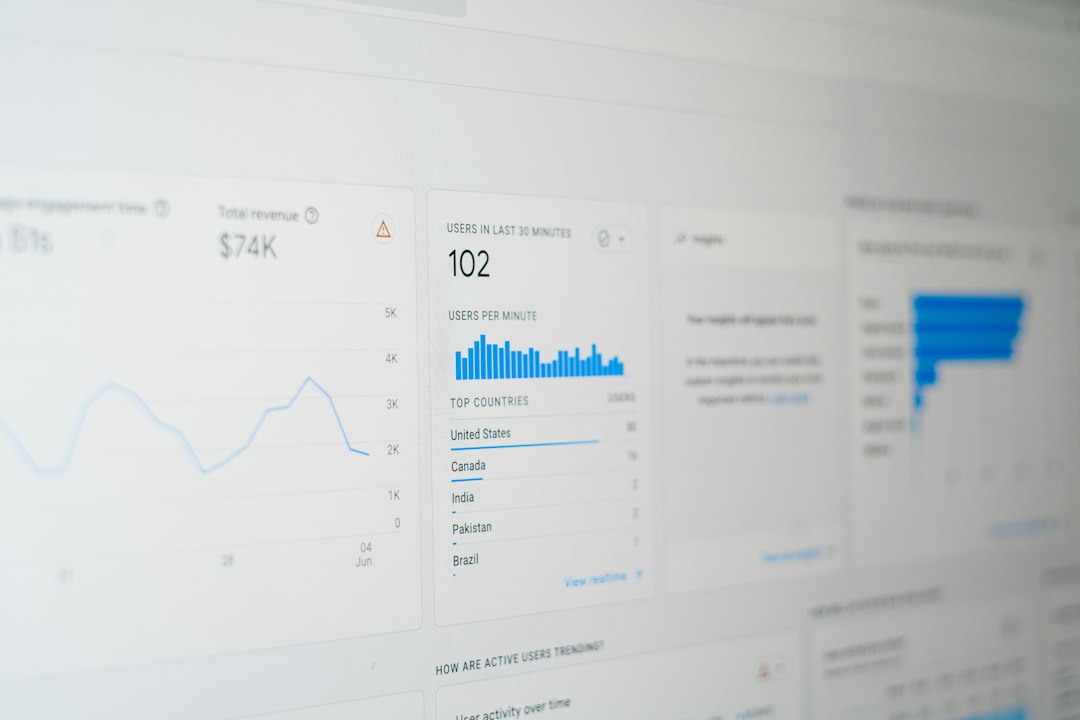
This approach stops GRC from becoming a filing cabinet. It also stops ERM from becoming a polished slide deck with weak data behind it. The goal is not more risk meetings. The goal is better decisions with proof attached.
FAQ
Is GRC part of ERM?
Often, yes. GRC can be viewed as a control and compliance layer within the wider ERM program. ERM uses GRC data to understand how well key risks are being managed.
Can a company have GRC without ERM?
Yes, but it may miss broader threats. A company may track controls and pass audits while still ignoring strategic, financial, or external risks that could cause serious damage.
Can a company have ERM without GRC?
It can, but the ERM program may lack evidence. Without GRC, risk ratings may depend too much on opinion and not enough on control results, incidents, and audit findings.
Which is better for regulatory compliance?
GRC is better suited for regulatory compliance because it manages obligations, testing, issues, evidence, and reporting. ERM may still track compliance as a top enterprise risk.
Who should own GRC and ERM?
GRC is usually owned by compliance, legal, audit, or security teams. ERM is often owned by a chief risk officer, enterprise risk team, or executive risk committee with board oversight.
What is the ideal end state?
The ideal state is a connected model where GRC proves control performance and ERM turns that proof into business level risk decisions.